
cloud
Public Cloud Security Risks: Is Your Organization Prepared for Cloud Threats?
Most cloud breaches trace to misconfiguration, weak identity, and shared-responsibility gaps. Eight strategies, container security, and a readiness checklist.
Writing
Page 19 of 26.
Most cloud breaches trace to misconfiguration, weak identity, and shared-responsibility gaps. Eight strategies, container security, and a readiness checklist.
Startups have unique challenges when it comes to cybersecurity. If not taken seriously, they can lose customers and their trust.

The future of passwords is looking brighter than ever. With the rise of cyber-attacks and data breaches, it's becoming more important to use strong
Though zero trust architecture may be potent for reinforcing overall security, chances of sneaking and security breaches aren’t always zero.
Today's threat actors have become so sophisticated that they use a systemized modus operandi to target their next victim.
Federated SSO lets users authenticate across organizational boundaries via SAML or OIDC. When to use it, how it works, and what to evaluate in a platform.
Many people like starting a business because they feel they have a great idea or can do something better than someone else.
Data privacy is now a priority for enterprises to manage and address proactively.
Are you interested in getting involved in cybersecurity or tech start-ups? Learn about my story and how I got started in this short video.
The API best practices start with their structure, type, how to send and receive the data, security, performance, scaling, etc.
A set of protocols and definitions allows different programs to connect. An API is an outline that tells a developer how to build a program to communicate
I have spent over a decade building consumer identity infrastructure. Here is how privacy went from compliance line-item to product strategy.
As cyberspace has evolved and matured, the role of the CTO has become increasingly demanding due to the business-damaging nature of cyber threats, which
The answer lies with data-informed decision-making and strategic execution. Achieving this is easier said than done: It requires changing how enterprise
Authentication, identity verification, and identification answer three different security questions. Confusing them is how products end up with weak controls.
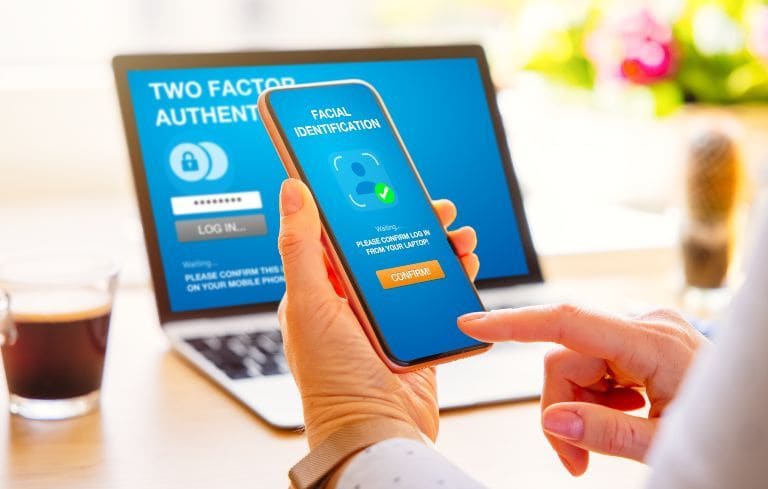
Out-of-band authentication adds a second communication channel to verify the user. Here is how it works and where it earns its keep.
Traditional IAM was built for employees, not customers. Here are five signs your IAM cannot do the CIAM job and what to fix.
In the past ten years, the rise of privacy-conscious consumers and emerging data regulations have compelled enterprises to prioritize their data
In any organization, a CTO has to wear multiple thinking hats to steer product development, build cybersecurity defenses, navigate uncertainty and drive
Most B2B SaaS companies bolt on identity as an afterthought. After scaling a CIAM platform to 1B+ users, I learned that getting identity right from the
Single sign-on and social login both reduce password friction, but they solve different problems. Here is when to use each.

This post covers the aspects of the green cloud and how businesses can put their best foot forward in adopting these practices to shape the future of a
Cross-device authentication promises one identity across phones, laptops, and TVs. The privacy trade-offs deserve a hard look.
While businesses embark on a digital transformation journey, cloud adoption is undoubtedly the cornerstone for new-age enterprises.

Businesses need to gear up for the new reality and ensure they create a seamless user experience by adhering to privacy and compliances while delivering a

This article discusses the aspect of botnet attacks and why businesses should put their best efforts into minimizing the risk.
OAuth 2.0 client credentials grant explained: how services authenticate to each other, request scoped tokens, and call APIs without a user in the loop.
Enterprises have already started to embrace zero trust security over traditional security since it offers improved security while simultaneously improving
Most Drive exposures come down to unenforced 2-Step Verification and nobody auditing external sharing. Here are the seven mistakes and the fixes.
The rapid progression of artificial intelligence (AI) technology has left researchers and governments debating the need for a regulatory framework.