
Latest
cybersecurity
Top 5 Bug Bounty Platforms for Security Researchers in 2026
HackerOne, Bugcrowd, Intigriti, Synack and YesWeHack compared: payouts, triage, AI bug bounty scope, and where to start at your skill level.
Read the articleTag
All topics →Everything tagged access control.
26 stories, newest first.
Latest
HackerOne, Bugcrowd, Intigriti, Synack and YesWeHack compared: payouts, triage, AI bug bounty scope, and where to start at your skill level.
Read the articleThe scoring sheet for a CIAM evaluation: 25 capabilities to test every vendor against, weighted by business type, verified for 2026.
Twenty-five capabilities that separate a PAM platform that works from one that gets shelved, from discovery and vaulting through just-in-time access, session recording, and threat analytics.
ADManager Plus, ADAudit Plus, SentinelOne, NinjaOne, and free tools from Netwrix and SolarWinds compared for AD admin, auditing, and security.
Okta alternatives for workforce identity compared: Entra ID, Rippling, JumpCloud, Ping, OneLogin, Duo and more, with verified 2026 pricing and best-fit picks.

Which cloud directory should you pick? JumpCloud, Entra ID (formerly Azure AD), Okta, Google Cloud Identity and four more, compared on protocols, devices, and price.
Age assurance vendors compared on independent certification, estimation accuracy and published pricing, plus the laws in force in September 2026.
Five credential management platforms compared on PKI lifecycle, FIDO2 and passwordless, post-quantum readiness, NIST 800-63 assurance levels and real pricing.
Top 10 PAM platforms for 2026, verified September 2026: vaulting, session recording, JIT access, secrets, pricing, and the CyberArk and StrongDM deals.
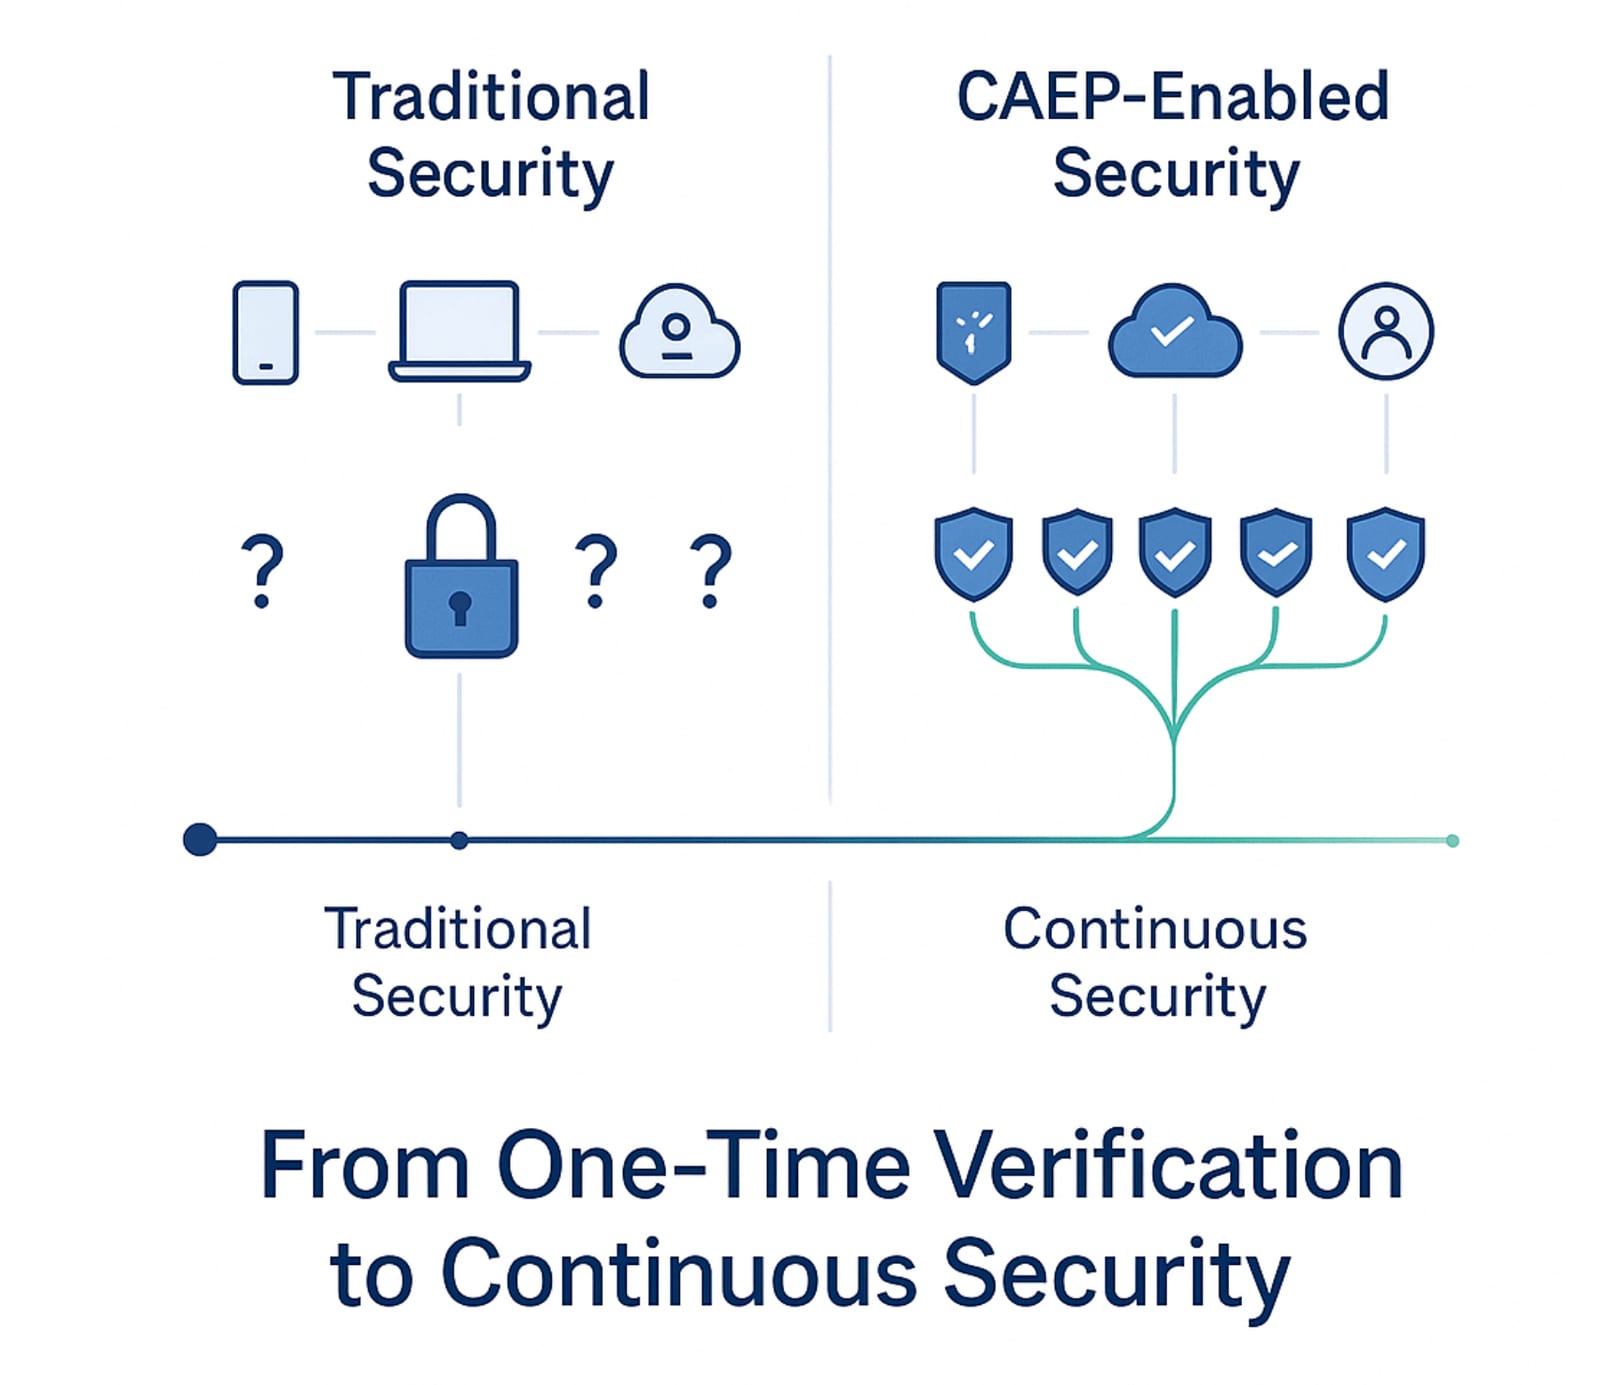
Most apps check user trust once during login, then ignore security changes for hours or days.
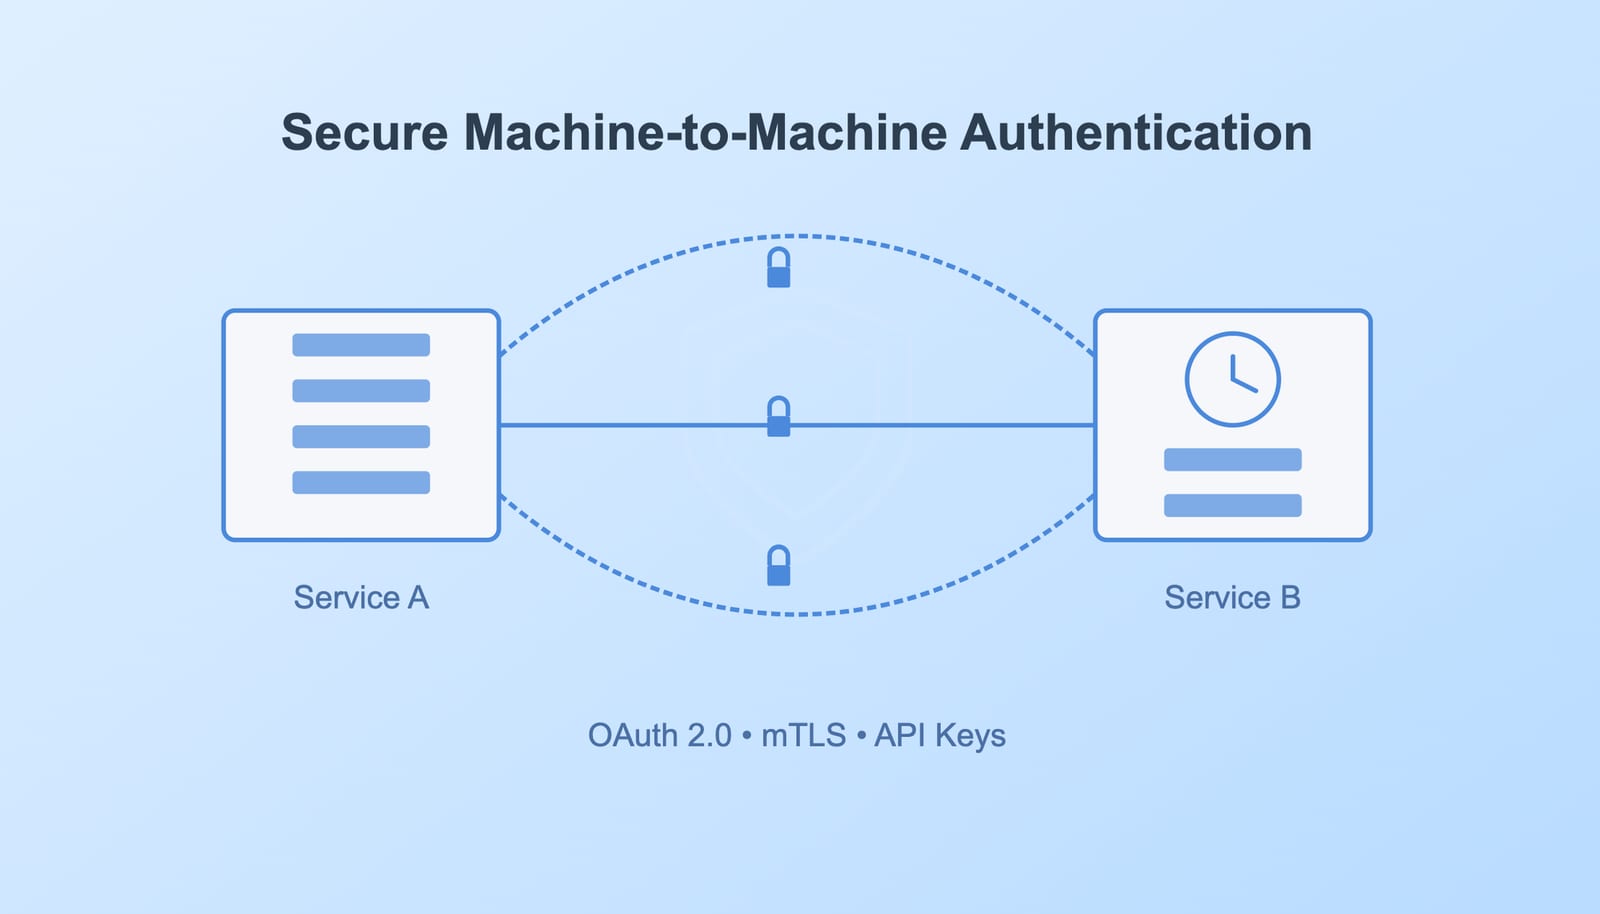
Machines talk to machines without human intervention. But how do you ensure these automated conversations remain secure?
IASM discovers every identity in your estate, maps what each can reach, and closes the paths attackers use. How it relates to ITDR, ISPM, CIEM and NHI security.
This guide explores SAML, OAuth, and SCIM protocols central to enterprise single sign-on (SSO) systems.
Learn how to secure your company's digital assets in just 10 minutes a day. This practical guide shows small business owners and startup founders how to
Transform your company's digital security from chaos to control with a access management system.
When a former employee retains access to sensitive systems months after leaving, it's more than a security oversight, it's a serious business risk.
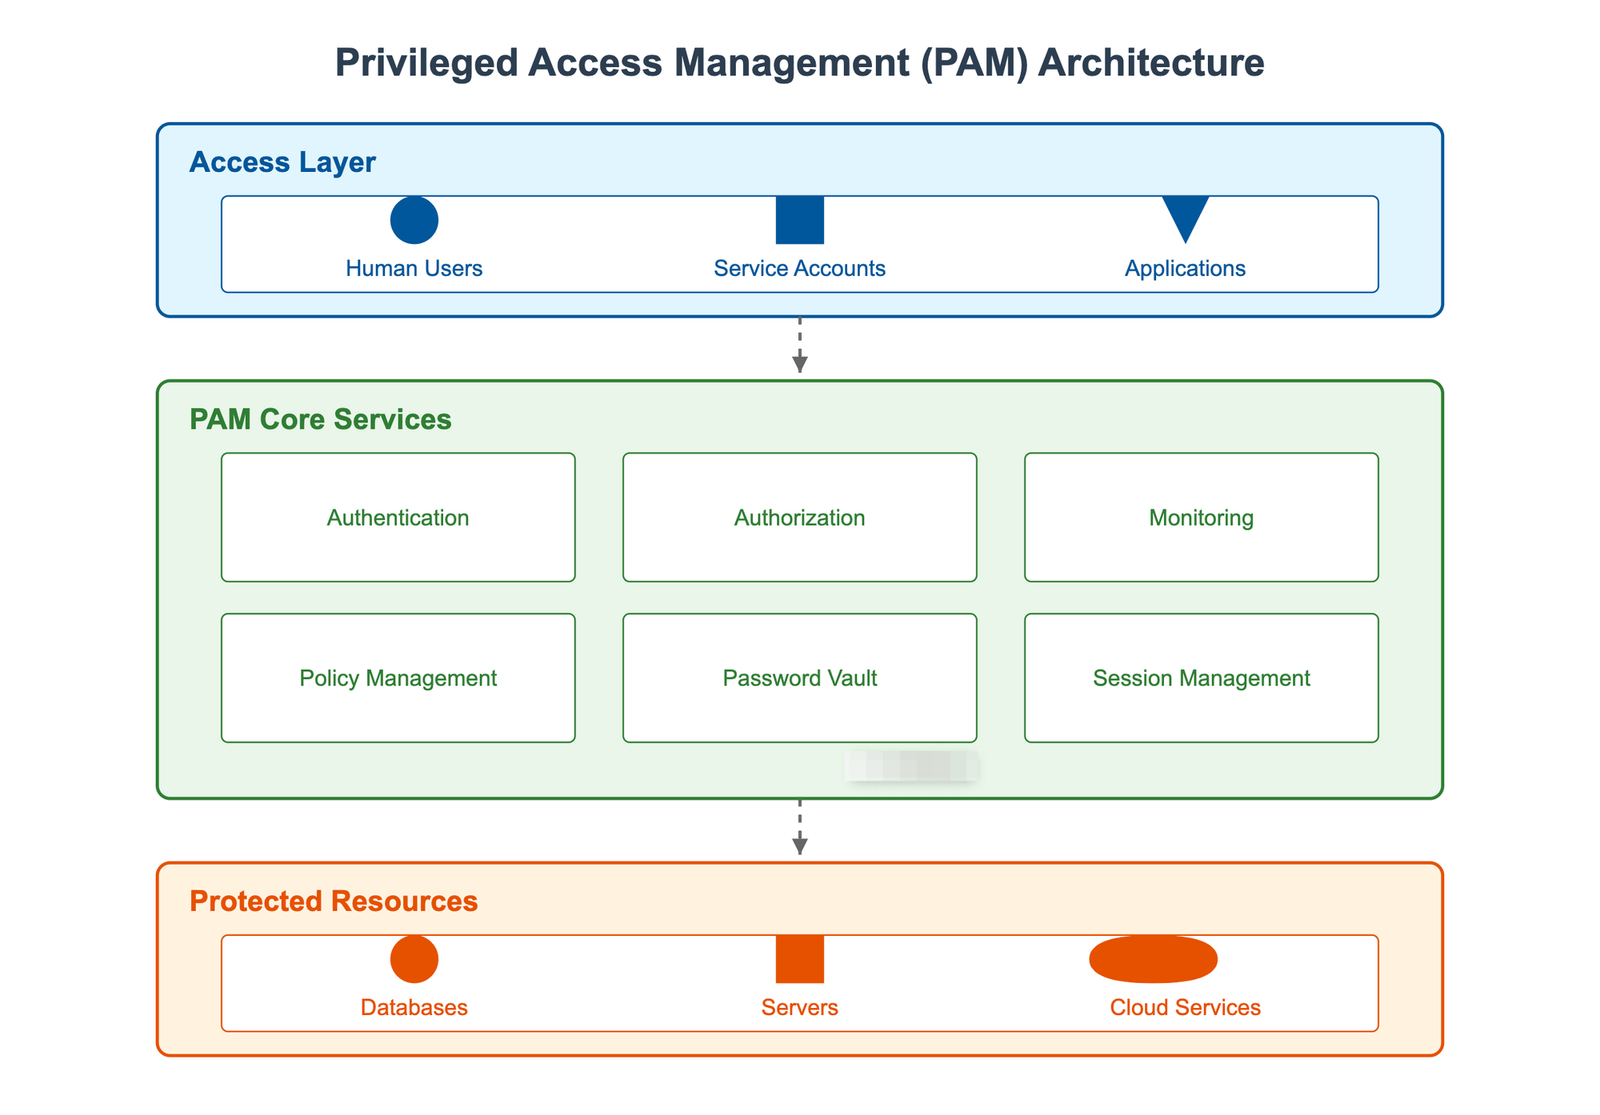
Privileged Access Management (PAM) is crucial in today's threat landscape. This guide explores what PAM is, why it's essential for your organization, and
As artificial intelligence evolves, the concept of "identity" extends beyond humans. This article delves into the technical intricacies of non-human
Identity and Access Management (IAM) is vital for organizations to safeguard their digital assets.
SCIM automates user provisioning and de-provisioning across cloud apps through a standard JSON schema and REST API. Here is how SCIM 2.0 actually works, how it differs from SSO, and why de-provisioning is the part that matters most.
AI revolutionizes access management by enabling intelligent provisioning, dynamic access control, and fraud prevention.
This essential CSO guide outlines the robust account monitoring, access notifications, multi-factor authentication, deception technology, and user
In the fast-paced world of the internet, where every click, every search, and every interaction leaves a digital footprint, the security of human
Discover the power of federated identity management for seamless SSO and enhanced user access. Improve security and streamline authentication
Most Drive exposures come down to unenforced 2-Step Verification and nobody auditing external sharing. Here are the seven mistakes and the fixes.
Exploited vulnerabilities overtook stolen credentials as the top way in, and most breached firms had not encrypted the data. Seven practices that work.