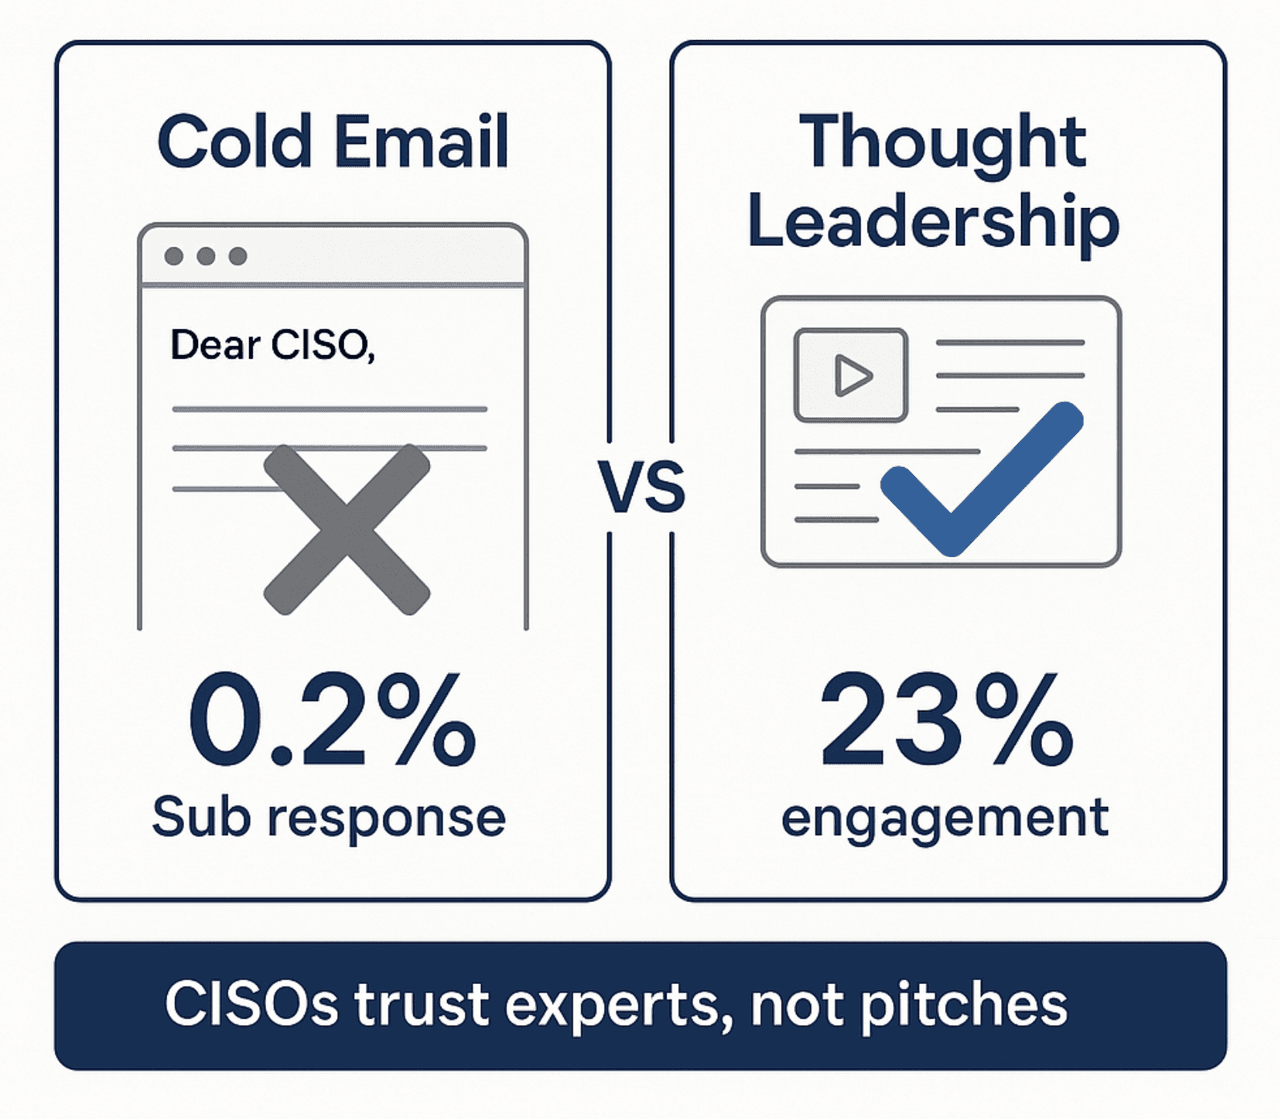
Security practitioners are professionally trained to distrust claims, which makes them the hardest audience in B2B for conventional content marketing. The way through is not better persuasion. It is content specific enough to be checked.
CrowdStrike clocks 29-minute breakout times and an 89% surge in AI-augmented attacks. Here is the five-phase framework I use with CISOs to close that gap, with budget splits and a board script.
Most cybersecurity vendors sell to the CISO and lose the deal to a security engineer they never spoke to. Security purchases are committee decisions with an asymmetric structure: many people can kill a deal, few can approve one. Here is how it actually works.
Your AI security review passed and still missed the real attack surface. EchoLeak, over-permissioned agents, shadow AI: the AI-specific vectors most CISOs never test for, and the five moves that close them.
Security leaders face over 10,000 alerts a day. Here is how to build a personalized cybersecurity news feed that filters the noise and surfaces the threats that matter to your organization.
B2B SaaS founders over-buy on 8 overlapping security tool categories and miss 4 that actually matter. Here's the stage-ranked shortlist of what to evaluate.
Security buyers research vendors in AI tools before a sales rep ever hears from them. The way a CISO interrogates ChatGPT looks nothing like how a marketer does. Here is what GEO actually looks like for cybersecurity.
Secure coding is cheaper than the alternative because defects found in design cost a fraction of defects found in production. Here are the principles, the OWASP Top 10 categories, and how to verify.
There has been an ongoing dialogue regarding the benefit of cybersecurity partnerships, with chief information security officers at the forefront of the