More than half of BIMI records are broken and nobody got an error. Silent failure is a whole category of security control, and most of yours are in it.
An enterprise prospect just asked for your SOC 2. Here is what the report really is, Type I vs Type II, the ten policies auditors expect, and how Vanta and Drata changed the work.
A stranger emails saying they found a security hole in your site and would like a reward. Is it a genuine researcher, a low-effort "beg bounty," or extortion? Here is how to tell the difference and exactly what to do and not do.
A founder's practical travel security checklist for 2026: realistic threats, what to actually do before, during, and after a trip, and where to skip the paranoia.
A founder's guide to the difference between authentication and authorization in 2026, with passkeys, agent auth, JWT pitfalls, and the mistakes I see at scale.
No single organization can defend against AI-powered attacks alone. Project Glasswing's $100M consortium model may be the template for the next decade of
The opinionated guide to running Claude Code well. CLAUDE.md, skills, subagents, hooks, and the workflows that produce quality code for engineers, QA, and
Vercel breached after attacker compromised Context.ai, hijacked an employee's Google Workspace via OAuth, and accessed customer API keys and environment
Claude Mythos discovered vulnerabilities that survived 27 years of human review. This technical breakdown covers how it works, what it found, and why your
Three AI framework attacks in one week expose how classic vulnerabilities are hiding in AI's foundational plumbing, putting millions of deployments at risk.
1Password for polish, Bitwarden for free and open source, Keeper for compliance. Ten password managers compared on verified 2026 pricing, audits and passkeys.
Proton VPN, Mullvad, IVPN and Windscribe are independent. Kape and Nord Security own five of the top ten. Ten VPNs compared on ownership, audits and price.
Zero Trust isn't magic. It's a specific set of architectural components working together, policy engine, identity fabric, device trust, microsegmentation,
AT&T's $177M settlement covers 73M customers, but the real story is how breach data from 2019 just resurfaced in 2026 with fully decrypted SSNs. Here's why.
Production authentication patterns for OAuth 2.0, OIDC, JWT, SAML, and WebAuthn, including the build-versus-buy maths and the storage and session decisions that are expensive to reverse later.
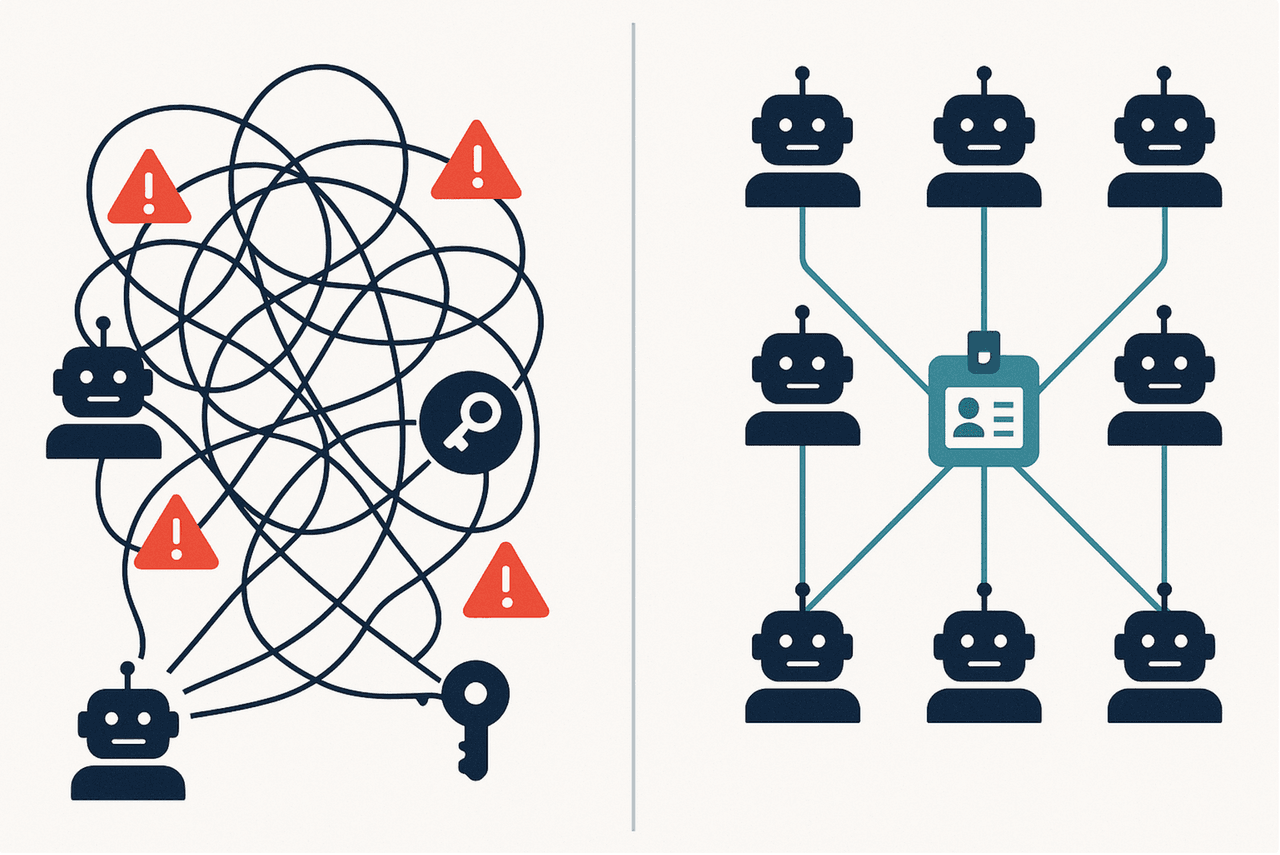
Struggling with MCP authentication? The November 2025 spec just changed everything. CIMD replaces DCR's complexity with a simple URL-based approach, no
Ten provisioning and access governance platforms compared on connectors, SCIM support, certification and separation of duties, verified September 2026.
Your firewall can't protect data from rogue admins or compromised systems. TEEs create hardware-secured "safe rooms" inside processors - protecting your
Master personal data security using Six Thinking Hats methodology. This strategic framework examines data protection through six distinct perspectives -
Discover API security strategies for Identity and Access Management systems. This expert guide covers authentication protocols, authorization frameworks,
Every browser comparison argues about which to pick. This one is about the mechanisms underneath: how process isolation and sandboxing differ by engine, what each vendor's business model makes it collect, and why Chromium-based does not mean equivalent.
From Basic Auth’s simplicity to OAuth 2.0’s delegated muscle, this quick-read unpacks the strengths, gaps, and best-fit use cases of the four core REST
Authentication pages serve as both security checkpoints and critical SEO touchpoints. While 80% of data breaches involve compromised credentials, properly
The EU's Chat Control regulation is still being negotiated in August 2026, with encryption protections agreed but mandatory CSAM detection still an open question.
Secure coding is cheaper than the alternative because defects found in design cost a fraction of defects found in production. Here are the principles, the OWASP Top 10 categories, and how to verify.
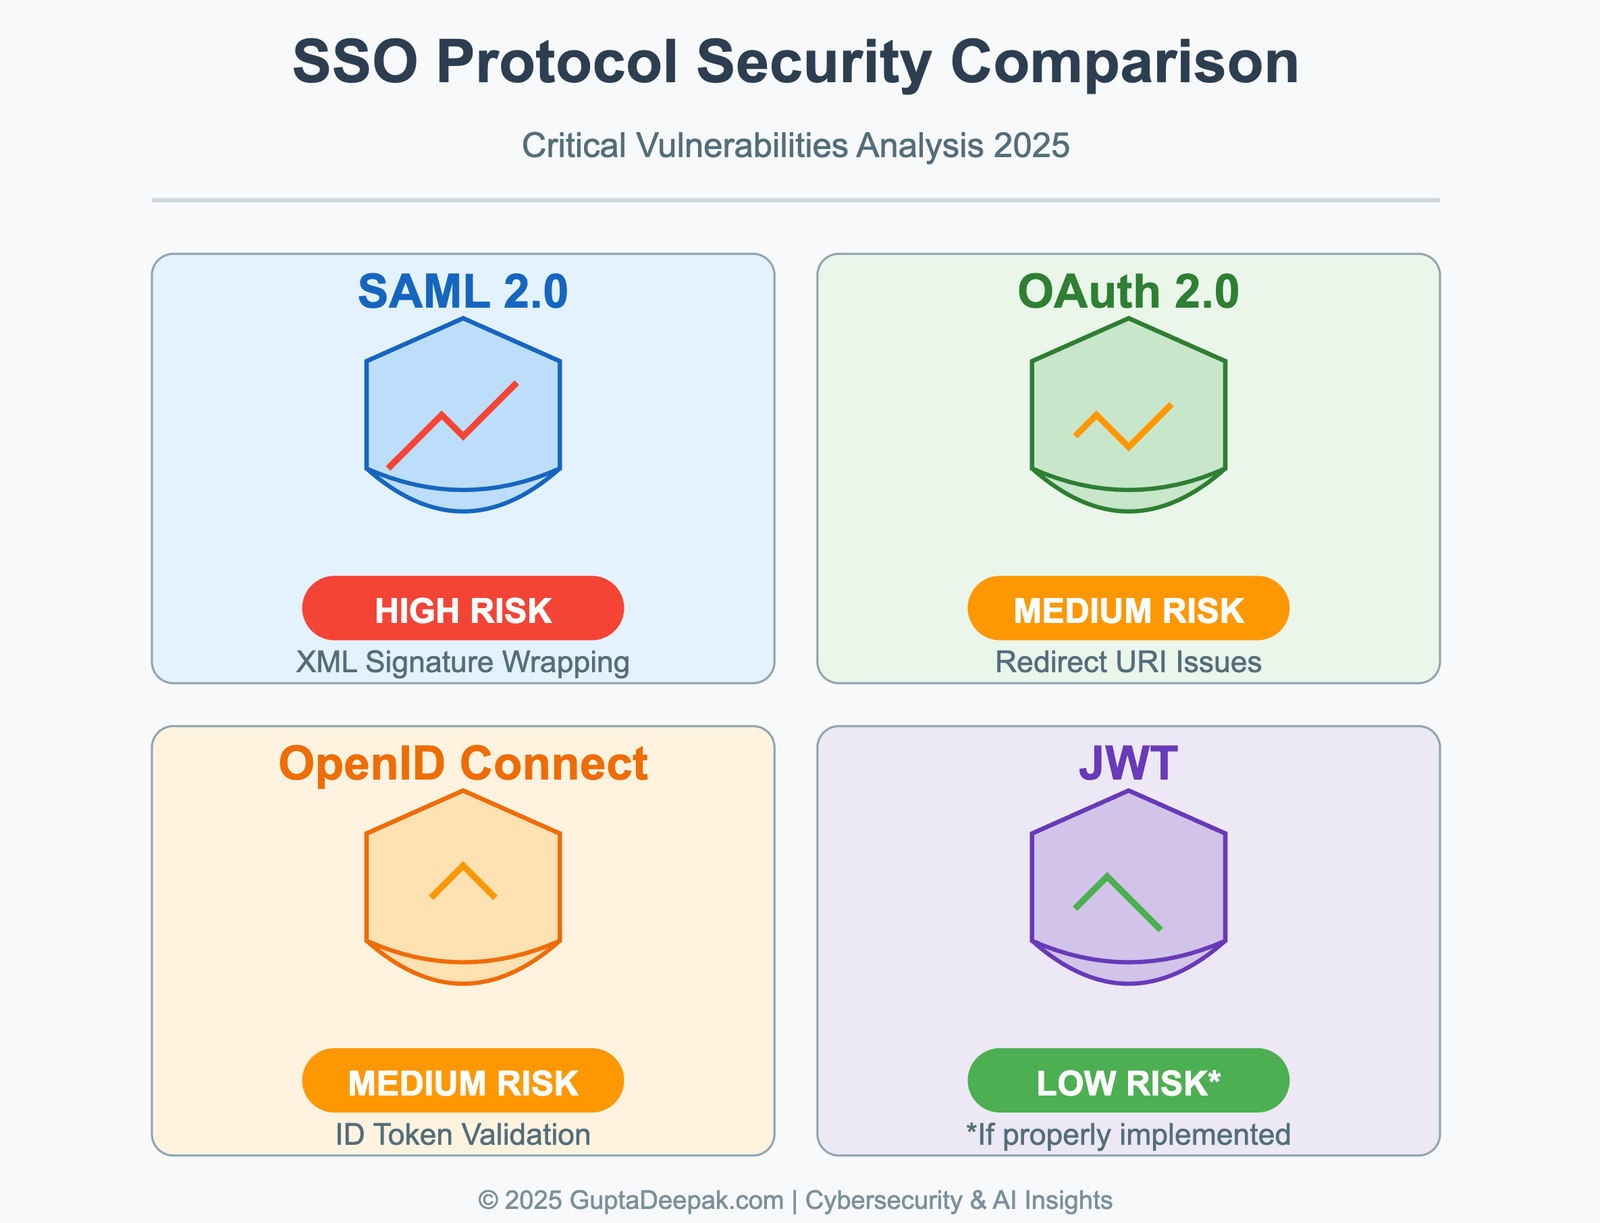
Discover which SSO protocols put your enterprise at highest risk. This data-driven analysis compares authentication vulnerabilities across SAML, OAuth,
Learn how to secure your company's digital assets in just 10 minutes a day. This practical guide shows small business owners and startup founders how to
Hashing is a fundamental concept in computer science and security. This comprehensive guide explores what hashing is, how it works, and its crucial role
Password security is paramount. Lets explore best practices for secure password storage, including use of robust hashing algorithms like bcrypt, scrypt,
The AI revolution in digital identity brings unprecedented security but at what cost? As AI systems become more sophisticated in protecting our digital
OTP fraud is on the rise. Can geo-fencing prevent it? Discover how this location-based technology helps, its limitations, and expert-backed strategies for
RESTful APIs are still vulnerable to various security risks. In this article, we will explore five common RESTful API security risks and discuss how to
More and more jurisdictions are only introducing new regulatory frameworks to protect consumer data, limiting enterprises in what data they can collect
As cyberspace has evolved and matured, the role of the CTO has become increasingly demanding due to the business-damaging nature of cyber threats, which
Protect your online activity and personal details to avoid identity fraud and cyber crimes - Tips on how to stay safe online and prevent identity theft,
With the rise in QR Code exploits, how can businesses and consumers decipher what a QR Code holds before scanning and mitigate the risks of a malicious QR
Gaining data visibility within an organization is quite beneficial for multiple reasons since the gathered data can be easily used to make more informed
Cookies vs. JWTs for authentication: how each works, where each fits, and why most modern systems run both side by side across web, mobile, and API surfaces.
DNS cache poisoning is an attack that uses changed DNS records to redirect online traffic to a website that is fake and resembles its intended destination.
It is hard to know what the data privacy landscape will look like in the future. As government regulations, like GDPR, continue to emerge, companies are
These easy login methods might be the nail in the coffin. We take a brief look at the death of passwords, and how to prepare for a passwordless future.
Business ventures concentrating on data first technique can altogether increase auxiliary income, cut expenses and accomplish faithfulness from their top
Almost every activity on the Internet requires that you fill in your email to gain access as most of the websites you visit ask for your email addresses
Introduction Because it makes the distribution and transmission of digital information much easier and more cost effective, multimedia has emerged as a
A passphrase of unrelated words beats a short random string, because length defeats brute force and memorability is what stops you reusing it. Here is what actually makes a password hard to crack.
Security as a gate at the end of the pipeline does not work. Here is the DevSecOps life cycle stage by stage, plus the culture changes that make it stick.
Data security is increasingly becoming a big problem for businesses of all kinds. Of course, as the world becomes increasingly digital, the danger present
In a surprising development around the Poly network hack, the officials offered the hacker to keep as much as $500K in reward after returning most of the
There has been an ongoing dialogue regarding the benefit of cybersecurity partnerships, with chief information security officers at the forefront of the
Implementing security procedures that emphasize potential dangers in cloud services can help you secure sensitive information and decrease threat risk.
The perimeter-based security model was built for a world that no longer exists. Zero trust replaces "trust but verify" with "never trust, always verify" -
Exploited vulnerabilities overtook stolen credentials as the top way in, and most breached firms had not encrypted the data. Seven practices that work.
Cloud security management is the practice of applying well-understood controls uniformly across a growing estate. What platforms do and what they cannot replace.
> Virtual networks are separated from other virtual networks and from the underlying physical network, offering the least privileged protection concept.
Security problems are an alternative way to recognise your customers when they have forgotten their password, entered too many times the wrong passwords,
Cloud security failures are almost always configuration failures. Five challenges that actually break companies and the certifications worth caring about.
> In relentless pursuit of automation and velocity, DevOps teams can reduce the software development cycle and ensure that their products are responsive
Whether you are a small enterprise, a large corporation, or something in between, phishing is one of the most damaging and vicious threats that you have
Every day, we are creating and sharing data at an astounding rate. With each email, text, tweet, tap and stream, more data is available for companies to
Put strong controls where ecommerce risk concentrates and keep them invisible to real shoppers: payment-page script rules, passkeys, bot management, governance.